Zero Trace Project
 Facebook ad: “Zero Trace Pen”
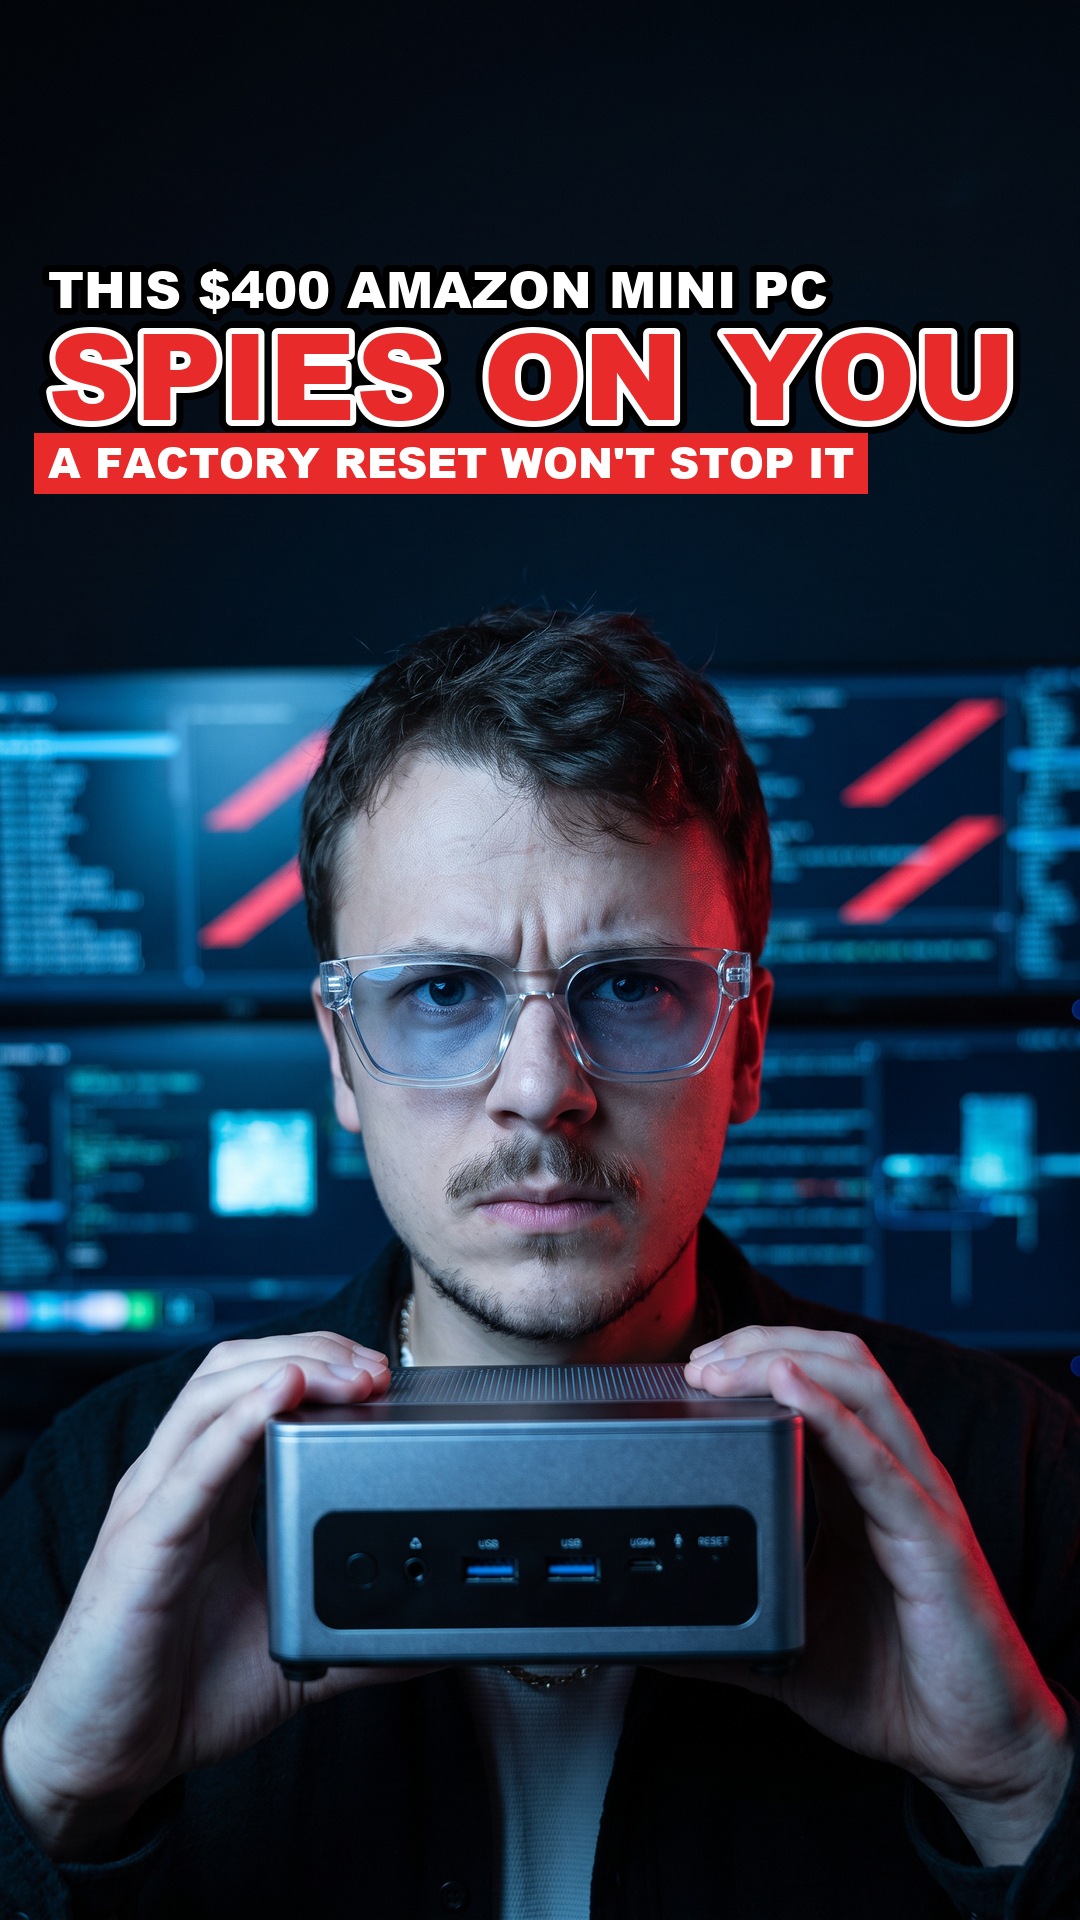
Ran for 13 days, from September 21 to October 4, 2026, the last day Crush saw it.
Run by Zero Trace Project on Facebook. Crush is not the advertiser and does not verify its claims. See this ad in Meta's Ad Library(opens in a new tab)
Make your own version of this ad
Crush makes it, launches it in your own Meta ad account, scales the winners and pauses the losers.
About this ad
- Meta Ad Library ID
- 1137995505558558
- Platforms
- Facebook, Instagram and Threads
- Relaunches
- 2
- EU reach
- 60
- Niche
- Finance & Trading
Ad text
Your cheap Amazon mini PC is a Trojan horse. AceMagic shipped mini PCs with two pieces of malware hand-coded into the Windows recovery partition. Not bloatware. Two executables, ENDEV.exe and EDIDEV.exe, written into the recovery image before the box was ever sealed. One was a Bladabindi remote access trojan, a full backdoor. The other was Redline, an info stealer that scrapes saved browser passwords, drains crypto wallets, and logs keystrokes. Here is what makes it nasty. It survives a factory reset. The malware lives inside the recovery image, so resetting the machine does not remove the infection, it reinstalls it. The one fix a normal person knows how to perform is the step that puts the trojan back. How does malware end up inside a factory recovery partition? Nobody paid for anything. No Microsoft license. Somebody pulled a cracked Windows installer off a forum and baked it into every drive they shipped. It is not one brand, either. The same parent company runs KAMRUI, NiPoGi and ACEMAGICIAN. Same factory, same playbook, same cracked image. To check your own machine: open File Explorer, go to the OS Windows version folder, and look for ENDEV.exe or EDIDEV.exe. If they are there, you are compromised. Do not touch the built-in factory reset. Boot from a clean Microsoft USB and wipe the drive yourself. But be honest about what that buys you. You are still running unlicensed Windows on hardware you cannot audit. No firmware verification. No clean BIOS. No visibility below the operating system. The reasoning that got people here sounded right and was completely wrong. Cheap plus isolated equals safe. Isolation is not a price point. A separate machine you do not control is not separate from anything, it is a second attack surface with your crypto wallet sitting on it. The Zero Trace Pen boots its own operating system entirely into RAM on any computer, even one with no hard drive. The host's Windows never runs. Tor by default. The MAC address rotates every session. Pull the pen and the session evaporates.
Where the ad sends people
zerotrace.org
Zero Trace Pen
Shop now: zerotrace.org(opens in a new tab)