Hossam K. Ahmed
 Facebook ad: “This content is provided strictly for educational and…”
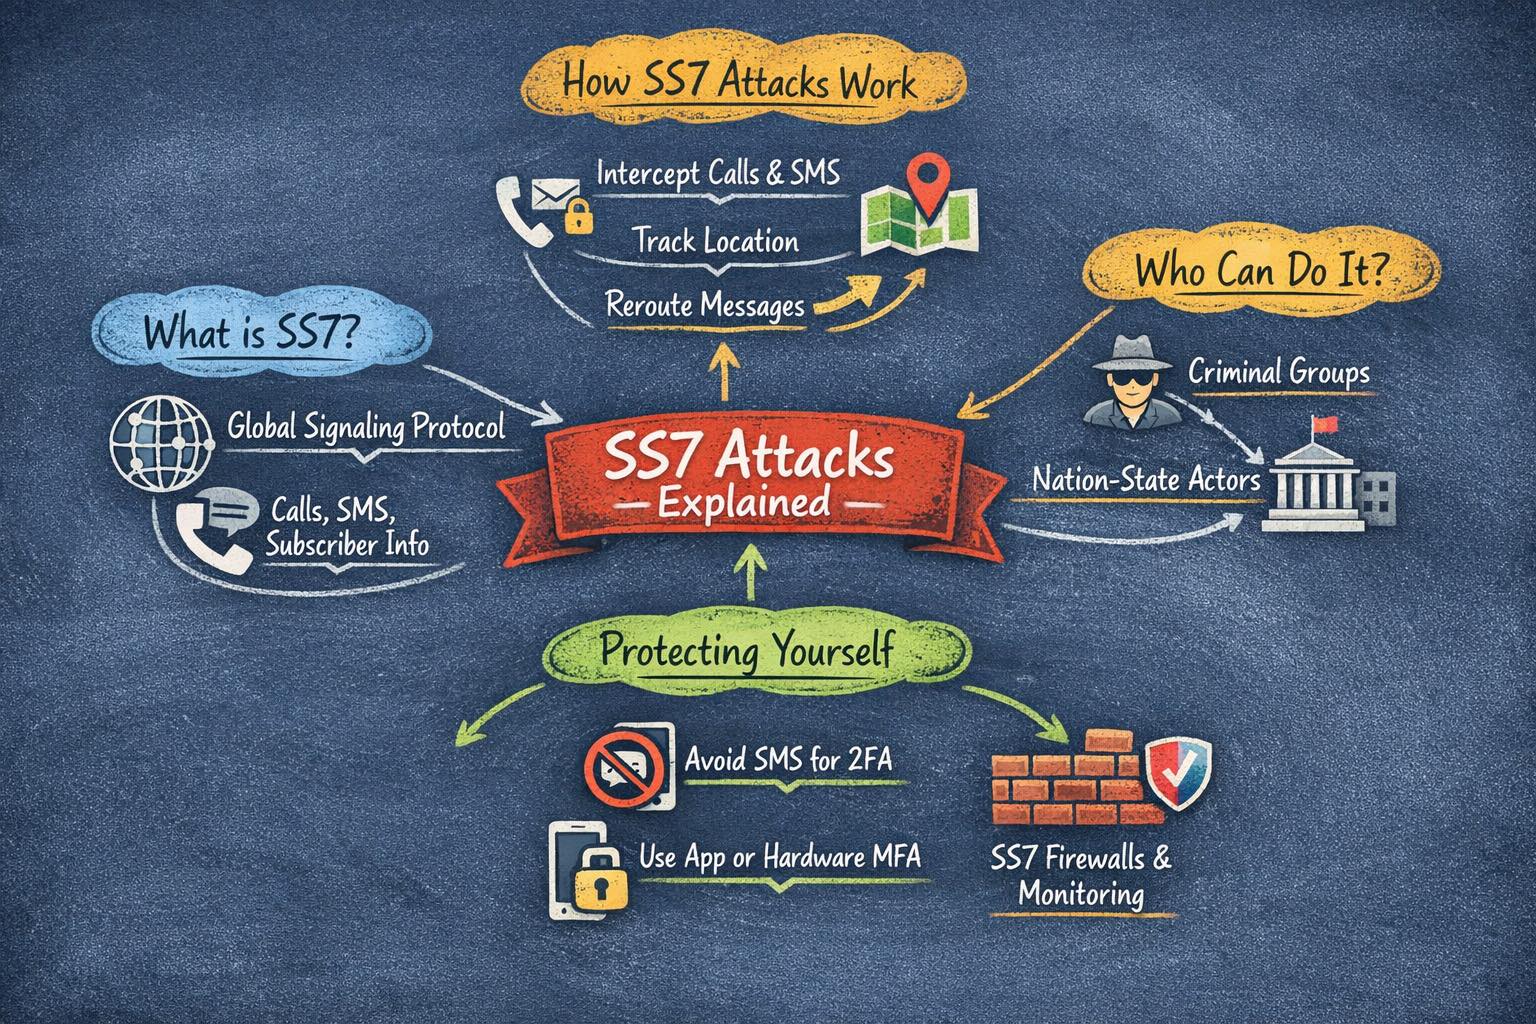
Ran for 55 days, from December 22, 2025 to February 15, 2026, the last day Crush saw it.
Run by Hossam K. Ahmed on Facebook. Crush is not the advertiser and does not verify its claims. See this ad in Meta's Ad Library(opens in a new tab)
Want an ad like this for your product?
Crush makes new ad images for your product from this ad: your logo, your product photo, your offer.
Trials from $19.95 USD, then $79.95 USD a month. Cancel anytime.
About this ad
- Meta Ad Library ID
- 2667543100289258
- Platforms
- Facebook, Instagram and Audience Network
- Relaunches
- 0
- Niche
- Jewelry & Watches
Ad text
This content is provided strictly for educational and informational purposes. It does not contain or endorse instructions for exploiting security vulnerabilities. What SS7 is: SS7 (Signalling System No.7) is the global signalling protocol used by telephone networks to set up/route calls, deliver SMS, handle roaming and lookup subscriber routing information. https://www.gsma.com/solutions-and-impact/technologies/security/t-isac-blog/ss7-securing-a-legacy-protocol-in-a-modern-threat-landscape-and-how-information-sharing-can-help-to-mitigate/ How SS7 attacks work: SS7 was built on mutual trust between carriers. If an attacker (or a compromised/rogue provider) can send messages onto the SS7 network, they can request a subscriber’s routing/location, re-route calls or SMS (including one-time codes), or manipulate message flows, enabling eavesdropping, SMS interception, or location tracking without touching the target’s phone. https://time.com/3641668/researchers-flaws-cellphone/ How likely / who can do this: Exploitation requires access to the signalling network or an intermediary who can send SS7 messages, this makes attacks practical for criminals who buy access, rogue operators, or well-resourced state actors, but not for a random internet script-kiddie. https://epic.org/documents/epic-v-cisa-ss7-cybersecurity-report/ What to do about it: Operators should deploy SS7/Diameter firewalls, strict peer vetting and anomaly detection, users should avoid SMS for critical 2-factor auth and prefer app-based or hardware MFA and end-to-end encrypted messaging for sensitive communications. https://www.gsma.com/solutions-and-impact/technologies/security/gsma_resources/fs-11-ss7-interconnect-security-monitoring-and-firewall-guidelines-v6-0/